Microsoft

Microsoft Surprises With Its First Server Linux Distribution: Azure Linux 4.0 (zdnet.com) 120

Microsoft is turning Azure Linux into a general-purpose, Fedora-based cloud distribution available to all Azure customers, while also productizing Flatcar as Azure Container Linux for immutable container hosts. "When Microsoft joined the Linux Foundation, there was this big conspiracy theory that somehow the Linux Foundation was undermining open source in partnership with Microsoft, and now you announce that you're shipping a Linux distribution," Jim Zemlin, the Linux Foundation's CEO, said in response to Microsoft's surprise announcement. "That's amazing." ZDNet reports: Until now, [Lachlan Everson, Microsoft's Principal Program Manager on Azure's open-source team] noted, "we had Azure Linux only available to third-party customers through AKS specifically, and that was Azure Linux 3.0." Going forward, this will be ACL. Everson emphasized that Azure Linux 4.0 is the culmination of years of internal usage and the evolution of the earlier Mariner distribution. "So we've been running Azure Linux for many years internally, and we got through to 3.0, and we only allowed it on as a container host on AKS. What we've done is make it a general-purpose, so this is all the learnings that we've had in the heritage of Mariner."

Under the hood, Azure Linux 4.0 is based on Fedora Linux and is delivered as an open distribution on GitHub. This code is available now. Yes, Red Hat knows that Microsoft has done this. Everson continued, "So, we made a decision to use Fedora as an upstream, so it's using RPMs in the Fedora ecosystem. Microsoft curates the packages and the supply chain to fit Azure's cloud platform." Microsoft also created "it to be purpose-built for Azure, which integrates vertically into all of our infrastructure to give you the best Azure Linux experience on Azure." While Azure Linux will ship as a VM image, Microsoft is already preparing a developer-friendly path onto Windows desktops: "And as of today, we have it as a VM image for your VM host on Azure. We're going to announce WSL images as well."

While developers will be able to run Azure Linux locally through WSL, Microsoft is not positioning it as a traditional desktop Linux. Asked whether he could run it on his laptop, Everson said: "I will be able to run it on my laptop, or what have you. Yes, on Windows 11." However, when pressed about a desktop experience, Everson was clear that there are "no plans" for a graphical environment. "It's optimized for server-side in the cloud," he said, adding that even on a developer machine, users should expect a lean environment. "Minimal packages, yeah. The idea is that we offer you a consistent experience to do your development on your machine, and that you can take your workloads as you develop them on your machine and run them with VS Code. You can run your applications on that, and know that the platform is the same that you're running on the cloud, so that you have that kind of consistency between environments."

Flatcar itself remains the upstream project, but Microsoft is packaging it for Azure customers. Everson described Flatcar as "purpose-built, immutable, secure by default, production-ready operating system, and Azure Container Linux is the productization of that, but we're still investing in the upstream Flatcar ecosystem and pulling that downstream into a productized exterior experience just for container workloads, so it's a container hosting in AKS." To underscore the immutable model, he added that "Everything's baked in, so there is no package manager. We bake the bits into the immutable, and they're in the immutable version. So Azure Container Linux is the immutable version. So you shouldn't be changing any system packages or any application packages. Anything that you need to change is customer workloads run in containers."

Security

New Windows 'MiniPlasma' Zero-Day Exploit Gives SYSTEM Access, PoC Released (bleepingcomputer.com) 32

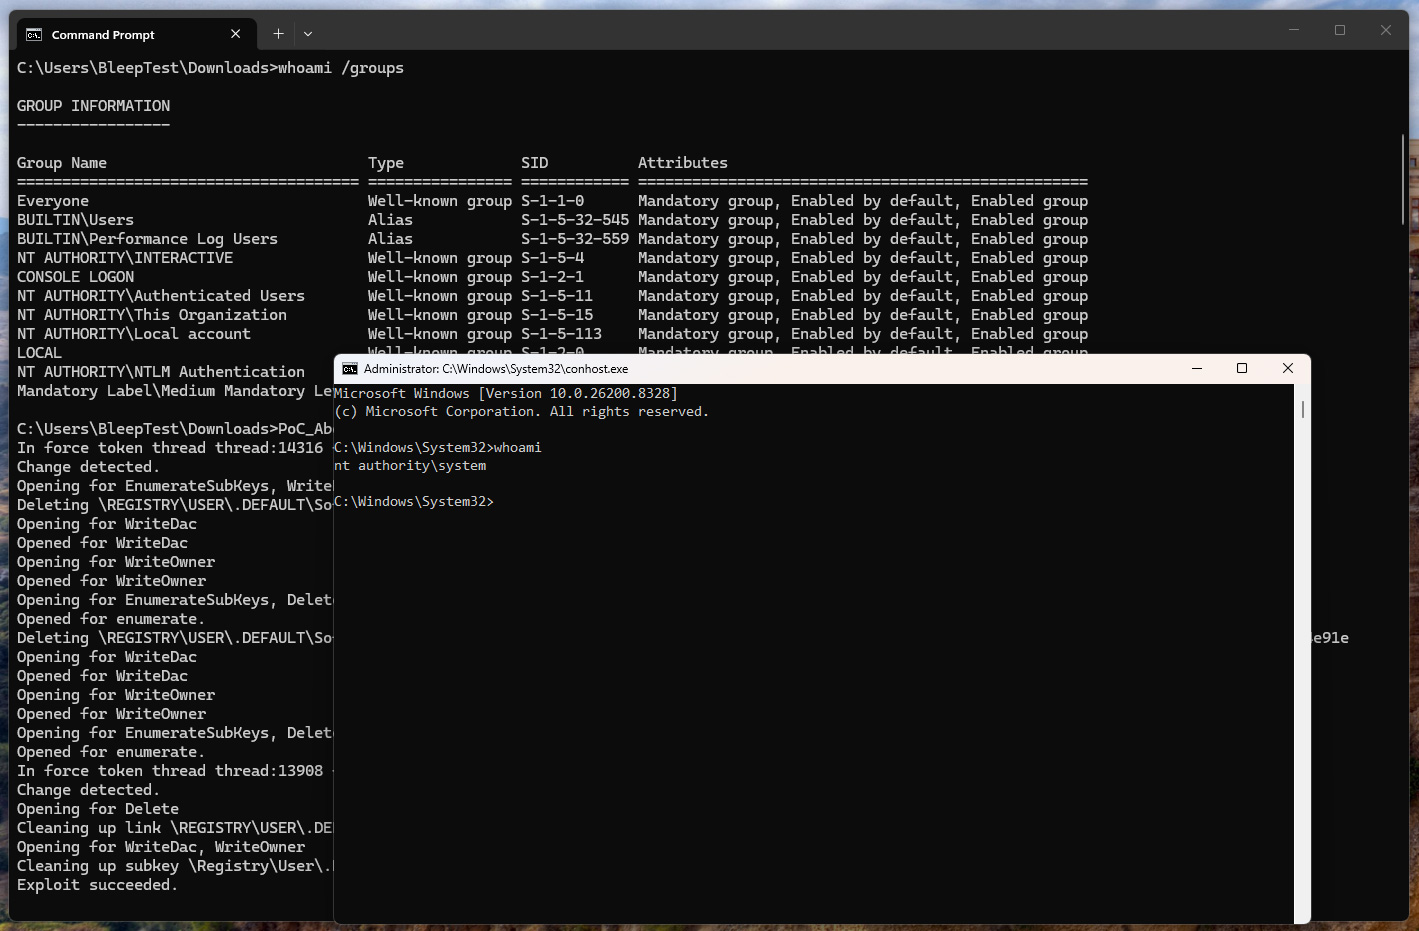
A researcher known as Chaotic Eclipse has released a proof-of-concept exploit for a new Windows zero-day dubbed MiniPlasma, which BleepingComputer confirmed can grant SYSTEM privileges on fully patched Windows 11 systems. The researcher claims the bug is effectively a still-exploitable version of a 2020 flaw Microsoft said it had fixed. From the report: At the time, the flaw was assigned the CVE-2020-17103 identifier and reportedly fixed in December 2020. "After investigating, it turns out the exact same issue that was reported to Microsoft by Google project zero is actually still present, unpatched," explains Chaotic Eclipse. "I'm unsure if Microsoft just never patched the issue or the patch was silently rolled back at some point for unknown reasons. The original PoC by Google worked without any changes."

BleepingComputer tested the exploit on a fully patched Windows 11 Pro system running the latest May 2026 Patch Tuesday updates. In our test, we used a standard user account, and after running the exploit, it opened a command prompt with SYSTEM privileges, as shown in the image [here]. Will Dormann, principal vulnerability analyst at Tharros, also confirmed the exploit works in his tests on the latest public version of Windows 11. However, he said that the flaw does not work in the latest Windows 11 Insider Preview Canary build.

The exploit appears to abuse how the Windows Cloud Filter driver handles registry key creation through an undocumented CfAbortHydration API. Forshaw's original report said that the flaw could allow arbitrary registry keys to be created in the .DEFAULT user hive without proper access checks, potentially enabling privilege escalation. While Microsoft reports having fixed the bug as part of its December 2020 Microsoft Patch Tuesday, Chaotic Eclipse now claims the vulnerability can still be exploited.

Microsoft

Microsoft Testing Adjustable Taskbar, Start Menu In Windows 11 (bleepingcomputer.com) 98

Microsoft is testing long-requested Windows 11 customization options, including a resizable taskbar, smaller taskbar buttons, and a more configurable Start menu that lets users reduce recommended content. BleepingComputer reports: Starting with Windows 11 Insider Preview Build 26300.8493, the taskbar can now be configured to use smaller buttons and moved to the bottom, top, left, or right side of the screen. "The ability to move the taskbar to the top or sides of the screen has been one of the most requested features, and we are bringing it to Windows 11," said Diego Baca, partner director of Microsoft Design. "With this update, when small taskbar is enabled, you get smaller icons, a shorter taskbar, and more vertical space for your apps (see video below). No restart or sign-out is required."

[...] Microsoft is also rolling out changes to give Windows users more control over the Start menu, allowing them to toggle off recommended content and customize its size. "These controls are designed to work together. If you want a Start menu with just your pinned apps, you can turn off Recommended and All," Boca added. "If you want a full Start that shows everything, you can leave it all on. The goal is simple: it is your choice, and it should be easy to make." However, Microsoft will maintain a list of recently installed apps, as it is a key way for users to discover new applications alongside the Microsoft Store.

Furthermore, Microsoft is improving file relevance by adjusting how files are displayed and ordered to prioritize the most relevant items, and will also allow users to hide their name and profile picture from the Start menu. [...] In addition to taskbar and Start menu improvements, the company plans to reduce notifications, simplify Windows settings, and ensure that device setup on new Windows PCs requires fewer reboots. Microsoft is also working on improving Windows search, aiming for a more consistent experience across the Start menu, taskbar, File Explorer, and Settings.

Microsoft

Microsoft Exchange Server Vulnerability Actively Exploited, in a Bad Week for Microsoft (securityweek.com) 12

Forbes describes it as "definitely already out there, and under active exploitation according to the U.S. Cybersecurity and Infrastructure Security Agency, urging all organizations to prioritize timely remediation as the attack vector poses a significant risk."

"We have issued CVE-2026-42897 to address a spoofing vulnerability affecting Exchange Outlook Web Access (OWA)," Microsoft told SecurityWeek. "We recommend customers enable EEMS to be better protected, and to follow our guidance available here." Microsoft this week patched 137 vulnerabilities with its Patch Tuesday updates and the cybersecurity industry was surprised to see that the latest updates did not address any zero-days. However, a zero-day was disclosed just 48 hours later, on May 14... described as a spoofing and XSS issue affecting Exchange Server Subscription Edition, 2016, and 2019. "Improper neutralization of input during web page generation ('cross-site scripting') in Microsoft Exchange Server allows an unauthorized attacker to perform spoofing over a network," Microsoft said in its advisory.

The company noted that the vulnerability affects Exchange Outlook Web Access (OWA) and an attacker can exploit it by sending a specially crafted email to the targeted user. "If the user opens the email in Outlook Web Access and certain interaction conditions are met, arbitrary JavaScript can be executed in the browser context," Microsoft explained.

CSO Online shares more details. "Admins should note there are known issues once the mitigation is applied either manually or automatically through the EM Service." - OWA Print Calendar functionality might not work. As a workaround, copy the data or screenshot the calendar you want to print, or use Outlook Desktop client.

- Inline images might not display correctly in the recipient's OWA reading pane. As a workaround, send images as email attachments or use Outlook Desktop client...

- Admins may get a message saying "Mitigation invalid for this Exchange version." in mitigation details. This issue is cosmetic and the mitigation does apply successfully if the status is shown as "Applied". Microsoft is investigating how to address this glitch.

Forbes notes "It's been something of a rough few days for Microsoft Exchange on the security vulnerability front," since this week also saw a zero-day demonstrated at the Pwn2Own Berlin hacking event, "which has been responsibly disclosed and not released into the wild." The Berlin event got off to a flying start on May 14 as Windows 11 was hit by no less than three zero-day exploits. On day two, hacking teams were no less successful, chaining together three new vulnerabilities in Microsoft Exchange in order to achieve the holy grail of SYSTEM-level remote code execution. Such was the level of this achievement that Orange Tsai from the DEVCORE Research Team was rewarded with a $200,000 bounty payment in return for immediately handing over all the technical details to the event organizers.
"This is, in fact, good news," Forbes writes, since "full details of the vulnerabilities underlying the exploits, along with the technical nature of the exploit code itself, will be handed over to Microsoft, which will then have 90 days to provide a fix before any details are made public."
United Kingdom

UK Antitrust Regulator Is Officially Investigating Microsoft Office (engadget.com) 58

The UK's Competition and Markets Authority is opening a formal investigation into whether Microsoft's bundling of Windows, Office, Teams, Copilot, and related products harms competition. Engadget reports: "Our aim is to understand how these markets are developing, Microsoft's position within them and to consider what, if any, targeted action may be needed to ensure UK organizations can benefit from choice, innovation and competitive prices," CMA Chief Executive Sarah Cardell said in a statement published by Reuters.

She also stressed the importance of the investigation by noting that hundreds of thousands of UK residents use business software and Microsoft products. The organization will take a look into the company's cloud licensing practices. The CMA has stated that the inquiry will conclude by February. At that point, Microsoft could get slapped with a strategic market label.

Microsoft says it's "committed to working quickly and constructively with the CMA to facilitate its review of the business software market." A strategic market designation doesn't automatically assume wrongdoing, but will give the CMA more leeway when conducting further interventions.

Security

Mystery Microsoft Bug Leaker Keeps the Zero-Days Coming (theregister.com) 69

An anonymous researcher known as Nightmare-Eclipse, who has already leaked several Windows zero-days this year, has disclosed two more: YellowKey and GreenPlasma. The Register reports: Nightmare-Eclipse described YellowKey as "one of the most insane discoveries I ever found." They provided the files, which have to be loaded onto a USB drive, and if the attacker completes the key sequence correctly, they are granted unrestricted shell access to a BitLocker-protected machine. When it comes to claims like these, we usually exercise some caution, as this bug requires physical access to a Windows PC. However, seeing that BitLocker acts as Windows' last line of defense for stolen devices, bypassing the technology grants thieves the ability to access encrypted files. Rik Ferguson, VP of security intelligence at Forescout, said: "If [the researcher's claim] holds up, a stolen laptop stops being a hardware problem and becomes a breach notification."

Despite the physical access requirement, Gavin Knapp, cyber threat intelligence principal lead at Bridewell, told The Register that YellowKey remains "a huge security problem for organizations using BitLocker." Citing information shared in cyber threat intelligence circles, he added that YellowKey can be mitigated by implementing a BitLocker PIN and a BIOS password lock. Nightmare-Eclipse hinted at YellowKey also acting as a backdoor, allegedly injected by Microsoft, although the people we spoke to said this was impossible to verify based on the information available. The researcher also published partial exploit code for GreenPlasma, rather than a fully formed proof of concept exploit (PoC).

Ferguson noted attackers need to take the code provided by the researcher and figure out how to weaponize it themselves, which is no small task: in its current state it triggers a UAC consent prompt in default Windows configurations, meaning a silent exploit remains a work in progress. Knapp warned that these kinds of privilege escalation flaws are often used by attackers after they gain an initial foothold in a victim's system. "These elevation of privilege vulnerabilities are often weaponized during post-exploitation to enable threat actors to discover and harvest credentials and data, before moving laterally to other systems, prior to end goals such as data theft and/or ransomware deployment," he said. "Currently, there is no known mitigation for GreenPlasma. It will be important to patch when Microsoft addresses the issue."
The other zero-days leaked include RedSun, a Windows Defender privilege escalation flaw; UnDefend, a Windows Defender denial-of-service bug; and BlueHammer, a separate Microsoft vulnerability tracked as CVE-2026-32201 that was patched in April.

According to The Register, RedSun and UnDefend remained unfixed at the time of publication, and proof-of-concept code for the flaws was reportedly picked up quickly and abused in real-world attacks.
Microsoft

Windows Update Is Getting Automatic Rollbacks For Faulty Drivers (pcworld.com) 45

Microsoft is adding a Windows Update feature called Cloud-Initiated Driver Recovery that can automatically roll back faulty drivers to a previously known-good version without waiting for hardware makers or users to fix the problem manually. PCWorld reports: The way faulty drivers work today is that the hardware partner is responsible for pushing an updated driver, or the end user is responsible for manually uninstalling the problematic driver. "This creates a gap where devices may remain on a low-quality driver for an extended period," says the blog post. With Cloud-Initiated Driver Recovery, Microsoft will be able to remotely trigger a rollback of the faulty driver to a previously "known-good" version of the driver via the Windows Update pipeline. Microsoft says that testing and verification of Cloud-Initiated Driver Recovery will continue until August this year, aiming to deliver this feature to Windows PCs starting in September.
Security

Microsoft Issues Warning About Linux 'Copy Fail' Vulnerability (linux-magazine.com) 46

joshuark shares a report from Linux Magazine: Microsoft has issued a warning that a vulnerability with a CVSS score of 7.8 has been found in the Linux kernel. The vulnerability in question is tagged CVE-2026-31431 and, according to the Cybersecurity and Infrastructure Security Agency (CISA), "This Linux Kernel Incorrect Resource Transfer Between Spheres Vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise."

The distributions affected are Ubuntu, Red Hat, SUSE, Debian, Fedora, Arch Linux, and Amazon Linux. This could also affect any distribution based on those in the list, which means pretty much every Linux distro that isn't independent. The flaw is found in the Linux kernel cryptographic subsystem's algif_aead module of AF_ALG. The problem is that a particular optimization has led to the kernel reusing the source memory as the destination during cryptographic operations. What this means is that attackers can take advantage of interactions between the AF_ALG socket interface and a splice() system call. Until patches are released, Microsoft is advising that the affected crypto feature should be disabled, or AF_ALG socket creation should be blocked.
The vulnerability is also known as "Copy Fail," which has been shared on Slashdot and detailed in a technical report. The vulnerability affects almost every version of the Linux OS and is now being exploited in the wild. U.S. cybersecurity agency CISA has ordered all civilian federal agencies to patch any affected systems by May 15.
AI

Claude Managed Agents Can Engage In a 'Dreaming' Process To Preserve Memories 50

An anonymous reader quotes a report from Ars Technica: At its Code with Claude developers' conference, Anthropic has introduced what it calls "dreaming" to Claude Managed Agents. Dreaming, in this case, is a process of going over recent events and identifying specific things that are worth storing in "memory" to inform future tasks and interactions. Dreaming is a feature that is currently in research preview and limited to Managed Agents on the Claude Platform. Managed Agents are a higher-level alternative to building directly on the Messages API that Anthropic describes as a "pre-built, configurable agent harness that runs in managed infrastructure." It's intended for situations where you want multiple agents working on a task or project to some end point over several minutes or hours.

Anthropic describes dreaming as a scheduled process, in which sessions and memory stores are reviewed, and specific memories are curated. This is important because context windows are limited for LLMs, and important information can be lost over lengthy projects. On the chat side of things, many models use a process called compaction, whereby lengthy conversations are periodically analyzed, and the models attempt to remove irrelevant information from the context window while keeping what's actually important for the ongoing conversation, project, or task. However, that process, as I described it, is usually limited to a specific conversation with a single agent. "Dreaming" is a periodically recurring process in which past sessions and memory stores can be analyzed across agents, and important patterns are identified and saved to memory for the future. Users will be able to choose between an automatic process, or reviewing changes to memory directly.
Operating Systems

ReactOS Unifies Installation Media, Introduces GUI Installer and New ATA Driver (phoronix.com) 15

jeditobe writes: Developers of ReactOS told Phoronix that the project has introduced a unified BootCD, replacing its previously separate installation media and LiveCD images. The new image combines the traditional text-mode installer with a LiveCD mode in a single medium. Within this unified BootCD, the updated LiveCD mode now includes an option to launch a first-stage GUI installer. The graphical interface is intended to make installation more approachable for new users compared to the long-standing text-based setup process.

In a separate development, the project has also merged a new ATA storage driver that has been in progress since early 2024. The plug-and-play aware storage stack supports SATA, PATA, ATAPI, AHCI, and even SCSI devices, potentially expanding the range of hardware on which ReactOS can successfully boot.

Following recent improvements to graphics driver support, the project continues to make incremental progress across core subsystems, though its long development timeline remains a point of discussion. Will these usability and hardware compatibility improvements be enough to broaden ReactOS adoption beyond its current niche?

Please note that all new features are not present in version 0.4.15 and are available for testing in the latest nightly test builds.

Software

'Notepad++ For Mac' Release Is Disavowed By the Creator of the Original (arstechnica.com) 67

An anonymous reader quotes a report from Ars Technica, written by Andrew Cunningham: As its name implies, the venerable Notepad++ text editor began as a more capable version of the classic Windows Notepad, with features such as line numbering and syntax highlighting. It was created in 2003 by Don Ho, who continues to be its primary author and maintainer, and it has been a Windows-exclusive app throughout its existence (older Notepad++ versions support OSes as old as Windows 95; the current version officially supports everything going back to Windows 7). I'm not a devoted user of the app, but I was aware of its history, which is why I was surprised to see news of a "Notepad++ for Mac" port making the rounds last week, as though it were a port of the original available from the Notepad++ website.

Apparently, this news surprised Ho as well, who claims that the Mac version and its author, Andrey Letov, are "using the Notepad++ trademark (the name) without permission." "This is misleading, inappropriate, and frankly disrespectful to both the project and its users," Ho wrote. "It has already fooled people -- including tech media -- into believing this is an official release. To be crystal clear: Notepad++ has never released a macOS version. Anyone claiming otherwise is simply riding on the Notepad++ name."
Ho repeatedly asked the developer to stop using the brand and eventually reported the trademark use to Cloudflare, the CDN of the Notepad++ for Mac site. "Every day that website remains active, you are in further violation of the law," Ho wrote. "I cannot authorize a 'week or two' of continued trademark infringement."

Letov has since begun rebranding the app as "NextPad++," though the old branding and URL reportedly remained available. The name changes is "an homage to NeXT Computer," notes Ars, "and uses a frog icon rather than the Notepad++ lizard."
Role Playing (Games)

NetHack 5.0 Released (nethack.org) 46

"So yesterday the Devteam (it is always the Devteam) released version 5.0 of legendary and venerable rogueike compuer game NetHack," writes the Rogue-like games column @Play. "It is 39 years old..."

MilenCent (Slashdot reader #219,397) writes: In addition to play changes it's left for players to discover, this version updates the code to compile with C99, makes it much easier to cross compile the code for other systems than the one running, and now uses Lua for its dungeon generation. Happy hacking!
For new players, "Nethack 5.0 now has an optional tutorial in the early phases of the game that might help you," notes the Rogue-like games column @Play: Three systems binaries are provided: Windows, MS-DOS and Amiga. Yes, Nethack still supports MS-DOS, and yes, it still supports classic Amiga: it explicitly supports AmigaDOS 3.0, meaning it can still run on 68000 machines... That these are the only systems they provide binaries for shouldn't be seen as an indication that these are the "most important" platforms for Nethack, it's more that, since it's entirely open source, building it yourself is entirely possible, and more expected than with most software. Nethack can be built for Linux, Windows 8-11, AmigaDOS, MacOS (I'm not sure if this includes classic Mac too but it might), Windows CE (wow), OS/2 (additional wow), BeOS, VMS and multiple Unixes... Another option is to play through public Nethack servers. The most popular of these are probably alt.org and Hardfought.
XBox (Games)

Microsoft's Xbox Mode Is Now Available For All Windows 11 PCs (theverge.com) 27

Microsoft is rolling out Xbox mode to all Windows 11 PCs, bringing a full-screen Xbox PC app interface similar to Steam's Big Picture Mode. "Some players in select markets will be able to download the Xbox mode experience today, with availability expanding to more players in those markets over the next several weeks," says the Xbox team. The Verge reports: Xbox mode aims to try and bridge the gap between Xbox consoles and Windows, but its original debut felt like a beta on the Xbox Ally devices. "Since first introducing Xbox mode, formerly known as 'full screen experience,' on Windows handhelds, we've been listening closely to player feedback and continuing to evolve the experience across devices," says the Xbox team. "Those learnings directly shaped Xbox mode on Windows 11 PCs."

Microsoft is also rolling out improvements to the Xbox Ally X handheld today, including a preview of its Auto SR upscaling technology. Xbox console owners are also getting a new dashboard update today, with the ability to disable Quick Resume on individual games and a feature to add custom colors to the dashboard.

Ubuntu

Ubuntu's AI Plans Have Linux Users Looking For a 'Kill Switch' (theverge.com) 135

Canonical's plan to add AI features to Ubuntu has sparked pushback from users who are concerned it could follow Windows 11's AI-heavy direction. "After Canonical's announcement earlier this week that it's bringing AI features to Ubuntu, replies included requests for an AI 'kill switch' or a way to disable the upcoming features," reports The Verge. Canonical says it has no plans for a "global AI kill switch" but it will allow users to remove any AI features they don't want. From the report: In his original post, [Canonical's VP of engineering, Jon Seager] said the upcoming AI features will include accessibility tools like AI speech-to-text and text-to-speech, along with agentic AI features for tasks like troubleshooting and automation. Canonical is also encouraging its engineers to use AI more and plans to begin introducing AI features in Ubuntu "throughout the next year."

In a follow-up comment, Seager clarified that, "my plan is to introduce AI-backed features as a 'preview' on a strictly opt-in basis in [Ubuntu version] 26.10. In subsequent releases, my plan is to have a step in the initial setup wizard that allows the user to choose whether or not they'd like the AI-native features enabled." Ultimately, he said, "All of these capabilities will be delivered as Snaps to the OS, layered on top of the existing Ubuntu stack. That means there will always be the option of removing those Snaps."
Users who prefer to avoid AI entirely could switch to other distros like Linux Mint, Pop!_OS, or Zorin OS. "These distros have some similarities to Ubuntu, but may not necessarily adopt the new AI features Canonical is rolling out," adds The Verge.
OS X

Notepad++ Finally Lands On macOS as a Native App (nerds.xyz) 45

BrianFagioli writes: Notepad++ has finally made its way to macOS, and this time it is not through a compatibility layer. A new community-driven port brings the long-standing Windows text editor over as a fully native Mac application, built with Cocoa and compiled for both Apple Silicon and Intel systems. Instead of relying on Wine or similar tools, the project replaces the Windows-specific interface with a macOS-native one while keeping the core editing engine intact, allowing longtime users to retain the same workflow, shortcuts, and overall feel.

The port is independent from the original Notepad++ project but tracks upstream changes closely, with development happening in the open. It is code-signed and notarized, and notably avoids telemetry or ads. Plugin support is being rebuilt for macOS and is still evolving, but the groundwork is in place. While macOS already has several established editors, this effort is aimed squarely at users who want the familiar Notepad++ experience without relearning a new tool.
You can download the app here.
Ubuntu

Linux Version of Framework's Laptop 13 Pro is Outselling Its Windows Variant (pcworld.com) 68

Framework began shipping its new Laptop 13 Pro this week. And the Ubuntu variant is outselling the Windows variant, reports PC World: [I]t's selling quickly by Framework's internal metrics, with six batches of the Intel version of the laptop already sold out. [A later Framework social media post added "Spoke too soon, we're onto Batch 8."]

"Also nice validation of our approach, the Ubuntu configurations are outselling the Windows ones!"

That's not really surprising, for a few reasons. One, if you're buying a Framework laptop, you have a good reason to order it without an OS, even if you want Windows 11. It's easy to get it free or cheap elsewhere. (Framework says it's not counting the "None (bring your own)" option in these Ubuntu numbers.) Two, there are precious few places to order a new laptop with any kind of Linux pre-loaded — you've got Framework, a few smaller vendors like System76 and Slimbook, and a few models from Dell. Lenovo sold Ubuntu-loaded laptops at one point, but I can't find any on the site right now...

Perhaps it doesn't hurt that Microsoft and Windows are currently on a bit of an apology tour. After a couple of years of pushing hard on "AI" features that no one wants — not even the people who do want "AI" want the Copilot flavor — Microsoft is pulling back its integration into everything and now promising features that Windows has been missing ever since Windows 10.

Framework also reports that:
  • More than one third of purchasers say they're replacing a MacBook Pro, "and almost all of them are switching to Linux (based on our optional post-purchase survey)."
  • "Also in interesting sales data, the Gray/Black keyboard is vastly outselling the traditional Black one!"

Transportation

Is the World Ready For a Car Without a Rear Window? (msn.com) 139

There's a glass roof — but no rear-view window. Instead the Polestar 4 replaces the rear-view mirror with a live feed from a wide-angle camera. Its high-resolution display (1480 x 320 pixels) promises "a panoramic view of the outside," according to Polestar's web site, showing more of what's behind you. "Visibility in the dark and in rainy conditions is also vastly improved."

Besides the camera feed (and side mirrors), the Polestar 4 offers four short-range cameras (for 360-degree views), and even short-range ultrasonics, the Wall Street Journal points out. (Car rear-view windows are usually five feet off the ground, "making a typical traffic cone invisible from closer than about 35 feet." ) And this new design also improves "aero efficiency," reducing drag and shearing turbulence, "critical, since the Polestar 4 is all-electric, and aero drag is the mortal enemy of range." [A]s a practical matter, the Polestar 4's innovation only acknowledges what drivers already know. In many modern cars, the rearview mirror is all but useless, anyway. In a typical full-size SUV, the glass in the rear hatch is about 10 feet away from the rearview mirror, with two sets of headrests in between... Having spent a few days in what Polestar calls an "SUV coupe" I am here to report that drivers won't miss the mirror. For one thing, the display is shaped like a conventional mirror, imbuing it with the comfort of the familiar. The imagery is convincingly mirror-like — reversed — with eye-like focal length, decent resolution and lowlight sensitivity, making it easy to trust when judging distances, with the help of graphical overlays and warning tones. It also has excellent auto-dimming algorithms....

The Polestar 4 is called that because it is the fourth model from the Swedish-Chinese premium/luxury collab, born out of Volvo Cars' performance subbrand. Describing it as an "SUV coupe" almost feels like a translation error. The design eschews signaling traditional utility in favor of a jocund modernism — call it orbital chic.... As for missing the rear window, my advice is, don't look back.

"In sports cars, rearview mirrors have been essentially decorative for some time," the article points out. (The 1974 Lamborghini Countach LP400 originally envisioned "a rear-facing periscope fitted in a dorsal channel in the roof.")

"The era's contempt for rearview mirrors was captured in a scene from The Gumball Rally (1976) when Raul Julia's character snaps the mirror off his Ferrari Daytona and throws it away. 'The first rule of Italian driving,' he says. 'What's behind me is not important.'"

There's 11 exterior cameras, plus 12 ultrasonic sensors and a mid-range radar to watch for threats and "intervene if necessary". One feature even reads speed limit signs and shows the posted limit on the driver's display. ("If the car exceeds the limit, the driver will hear a warning sound.") Even the windshield has built-in camera sensors to provide automatically "adaptive" headlights that switch from high beam to low beam when they identify approaching vehicles or the taillights of cars ahead.

"A total of seven airbags are deployed in the event of a collision."

Thanks to Slashdot reader fjo3 for sharing the article.
Windows

Open Source Developer Brings Linux to Windows 95, Windows 98, and Windows ME (itsfoss.com) 37

Microsoft released the "Windows Subsystem for Linux" in 2016, adding an optional Linux environment into every operating system since Windows 10. But now an open source developer has brought Linux to Windows 95, Windows 98, and Windows Me, reports the blog It's FOSS, "with Linux kernel 6.19 running alongside the Windows 9x kernel, letting both operate on the same machine at the same time." A virtual device driver handles initialization, loads the kernel off disk and manages the event loop for page faults and syscalls. Since Win9x lacks the right interrupt table support for the standard Linux syscall interrupt, WSL9x reroutes those calls through the fault handler instead. Rounding it all out is wsl.com, a small 16-bit DOS program that pipes the terminal output from Linux back to whatever MS-DOS prompt window you ran it from.
The end result is that WSL9x requires no hardware virtualization, and can run on hardware as old as the i486, the article points out. On Mastodon the developer says they "really got this one in right under the wire, before they start removing 486 support from Linux."

The source code for WSL9x is released under the GPL-3 license, and was "proudly written without AI."
Hardware

Framework Laptop 13 Pro Is a Major Overhaul For the Modular, Upgradeable Laptop (arstechnica.com) 41

An anonymous reader quotes a report from Ars Technica: Framework has been selling and shipping its modular, repairable, upgradable Laptop 13 for five years now, and in that time, it has released six distinct versions of its system board, each using fresh versions of Intel and AMD processors (seven versions, if you count this RISC-V one). The laptop around those components has gradually gotten better, too. Over the years, Framework has added higher-resolution screens in both matte and glossy finishes, a slightly larger battery, and other tweaked components that refine the original design. But so far, all of those parts have been totally interchangeable, and the fundamentals of the Laptop 13 design haven't changed much.

That changes today with the Framework Laptop 13 Pro, which, despite its name, is less an offshoot of the original Laptop 13 and closer to a ground-up redesign. It includes new Core Ultra Series 3 chips (codenamed Panther Lake), Framework's first touchscreen, a new black aluminum color option, a larger battery, and other significant changes. And while it sacrifices some component compatibility with the original Laptop 13, displays and motherboards remain interchangeable, so Framework Laptop owners can buy the new Core Ultra board and owners of older Framework Laptop boards can pop one into a Pro to benefit from the new battery and screen. At 1.4kg (about 3 pounds), the Laptop 13 Pro is slightly heavier than the Laptop 13's 1.3kg, but it still stacks up well against the 14-inch M5 MacBook Pro (1.55kg, or 3.4 pounds).

The Framework Laptop Pro will start at $1,199 for a DIY edition with a Core Ultra 5 325 processor, and no RAM, SSD, or operating system. A prebuilt version with Ubuntu Linux installed will start at $1,499, and Windows 11 will cost another $100 on top of that. A Core Ultra X7 358H version starts at $1,599 for a DIY edition, and a "limited batch" Core Ultra X9 388H version starts at $1,799. A bare motherboard with the Core Ultra 5 325 starts at $449, while a Core Ultra X7 358H board will cost $799. Pre-orders are available now, and begin shipping in June.

Mozilla

Mozilla 'Thunderbolt' Is an Open-Source AI Client Focused On Control and Self-Hosting 23

BrianFagioli writes: Mozilla's email subsidiary MZLA Technologies just introduced Thunderbolt, an open-source AI client aimed at organizations that want to run AI on their own infrastructure instead of relying entirely on cloud services. The idea is to give companies full control over their data, models, and workflows while still offering things like chat, research tools, automation, and integration with enterprise systems through the Haystack AI framework. Native apps are planned for Windows, macOS, Linux, iOS, and Android. Thunderbolt allows organizations to do the following:
- Run AI with their choice of models, from leading commercial providers to open-source and local models
- Connect to systems and data: Integrate with pipelines and open protocols, including: deepset's Haystack platform, Model Context Protocol (MCP) servers, and agents with the Agent Client Protocol (ACP)
- Automate workflows and recurring tasks: Generate daily briefings, monitor topics, compile reports, or trigger actions based on events and schedules
- Work seamlessly across devices with native applications for Windows, macOS, Linux, iOS, and Android
- Maintain security with self-hosted deployment, optional end-to-end encryption, and device-level access controls

Slashdot Top Deals